- Published on
My AI coding agent setup: a MacBook controls, a home Windows PC runs
- Authors

- Name
- Nadim Tuhin
- @nadimtuhin
On this page
My laptop used to do everything. It ran the agents, held the repos and kept every terminal alive.
That meant three ways for work to stop. Close the lid and it stopped. Lose Wi-Fi and it stopped. Hit a rate limit on one account and, you guessed it, it stopped.
So I split the job in two. My MacBook Pro is the control room, where I type, plan, watch and review. A Windows PC at home is where the agents run. The payoff: I close the lid and the agents keep working, I reconnect from anywhere, and a rate limit on one account just moves the next request to another.
This post is the map. It covers what each piece does, why it's there, the order to build it in, and the traps worth knowing first. Each piece also has its own deep dive:
- Tailscale and Cloudflare Tunnel: reaching my home PC from anywhere with zero open ports
- Herdr: how my MacBook Pro connects to Ubuntu terminals on a Windows PC
- 9Router: one local endpoint in front of every AI coding account I have
- 9agent: run Claude Code, Pi or Hermes on any model with one command
- Hermes: the agent that runs my setup while I sleep, and learns from every correction
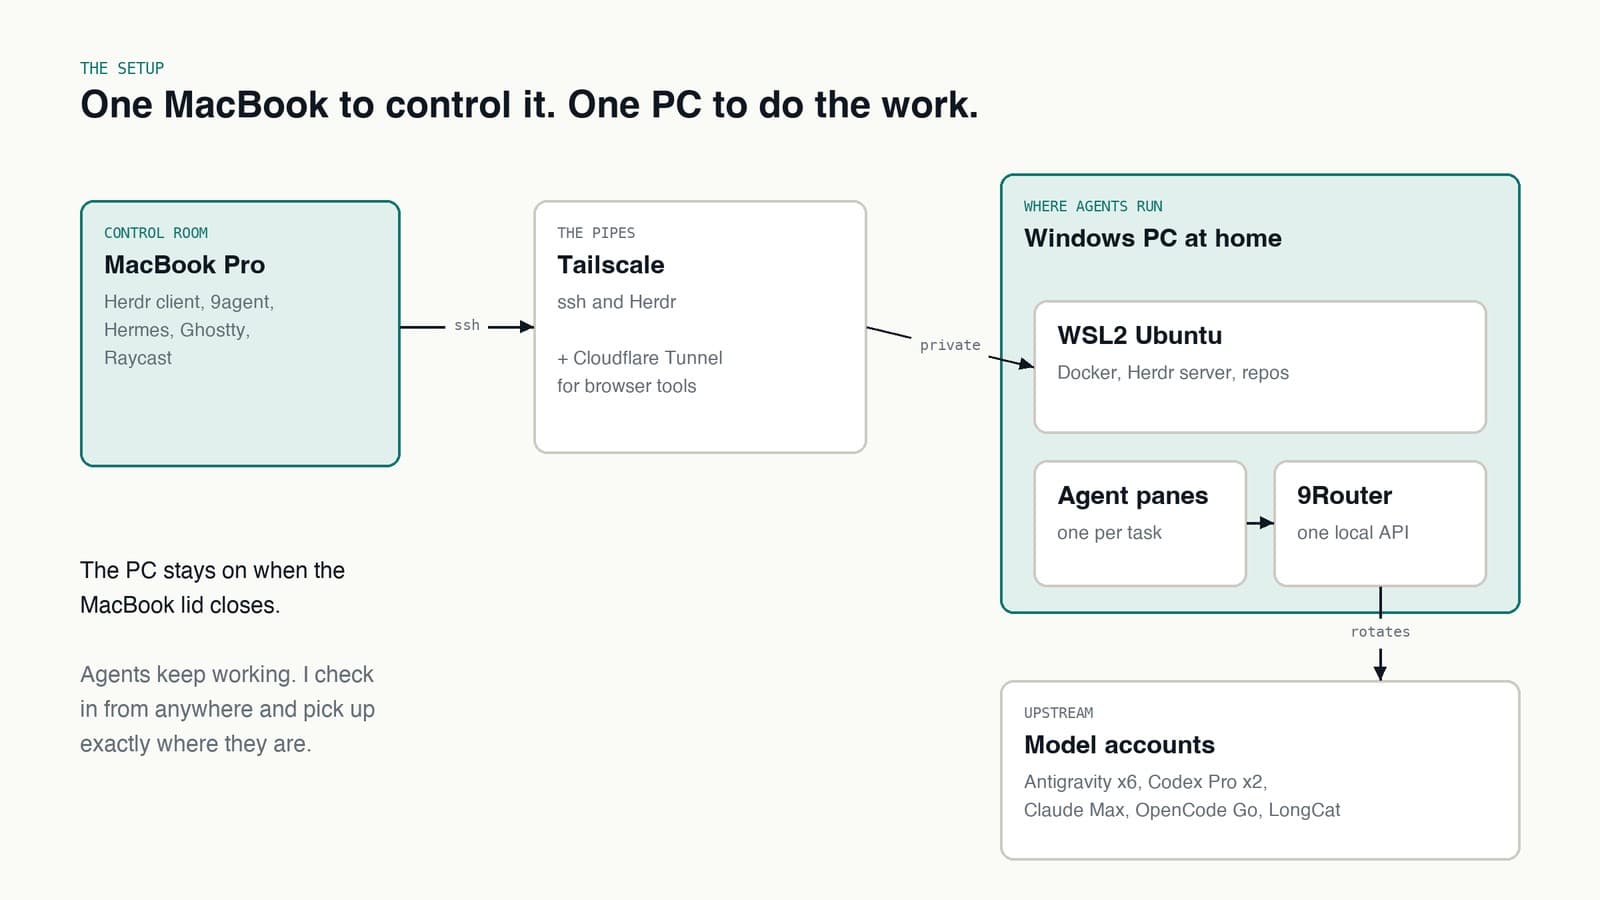
The setup at a glance
| Piece | Runs on | Its job |
|---|---|---|
| Herdr client, Ghostty, Raycast | MacBook Pro | My way into the PC's terminals, a keystroke away |
| 9agent | MacBook Pro | Start an agent against any model with one command |
| Hermes | MacBook Pro | Scheduled jobs and the assistant I talk to all day |
| WSL2 Ubuntu, Docker, repos | Windows PC | Where every agent process actually runs |
| Herdr server | WSL2 Ubuntu on the PC | Keeps the terminals alive when the MacBook is closed |
| Tailscale | Both machines | Private network for ssh, Herdr and 9Router |
| Cloudflare Tunnel | The PC, via cloudflared | Browser tools on my own subdomains, behind a Cloudflare Access login |
| 9Router | The PC | One endpoint in front of every model account |
The MacBook Pro: where I control everything
The MacBook Pro doesn't run the heavy work anymore. It runs the things I touch:
- The Herdr client, connected to the Ubuntu terminals on the PC
- 9agent, to start a new agent against any model with one command
- Hermes, for scheduled jobs and the assistant I talk to all day
- Ghostty and Raycast, so getting to any of it is a keystroke away
Nothing heavy runs locally, so the battery lasts, the fans stay quiet and closing the lid costs nothing. Everything I need is a terminal pane away, wherever I am.
The PC that does the work
It's a normal Windows desktop. Inside it, WSL2 runs Ubuntu, and Ubuntu runs Docker, the repos and every agent process.
Two rules keep it boring:
- Docker runs inside Ubuntu, not Docker Desktop. One engine, managed by systemd, no surprises after a Windows update.
- Every container has a memory and CPU limit. 16 GB goes fast when several agents and a browser run at once. With limits, one runaway process can't take the rest down.
Getting in from anywhere: Tailscale and Cloudflare Tunnel
My home router has no open ports. There are two ways in, and each has one job.
- Tailscale is for my own devices. It puts the MacBook Pro and the PC on a private network, so
ssh homelabworks the same from home, a cafe or a hotel. Herdr and 9Router ride on that connection. None of it is public. - Cloudflare Tunnel is for the browser.
cloudflaredon the PC makes an outbound connection to Cloudflare, which serves a browser editor and a view of a running browser on my own subdomains. Cloudflare Access asks me to sign in before any request reaches the PC.
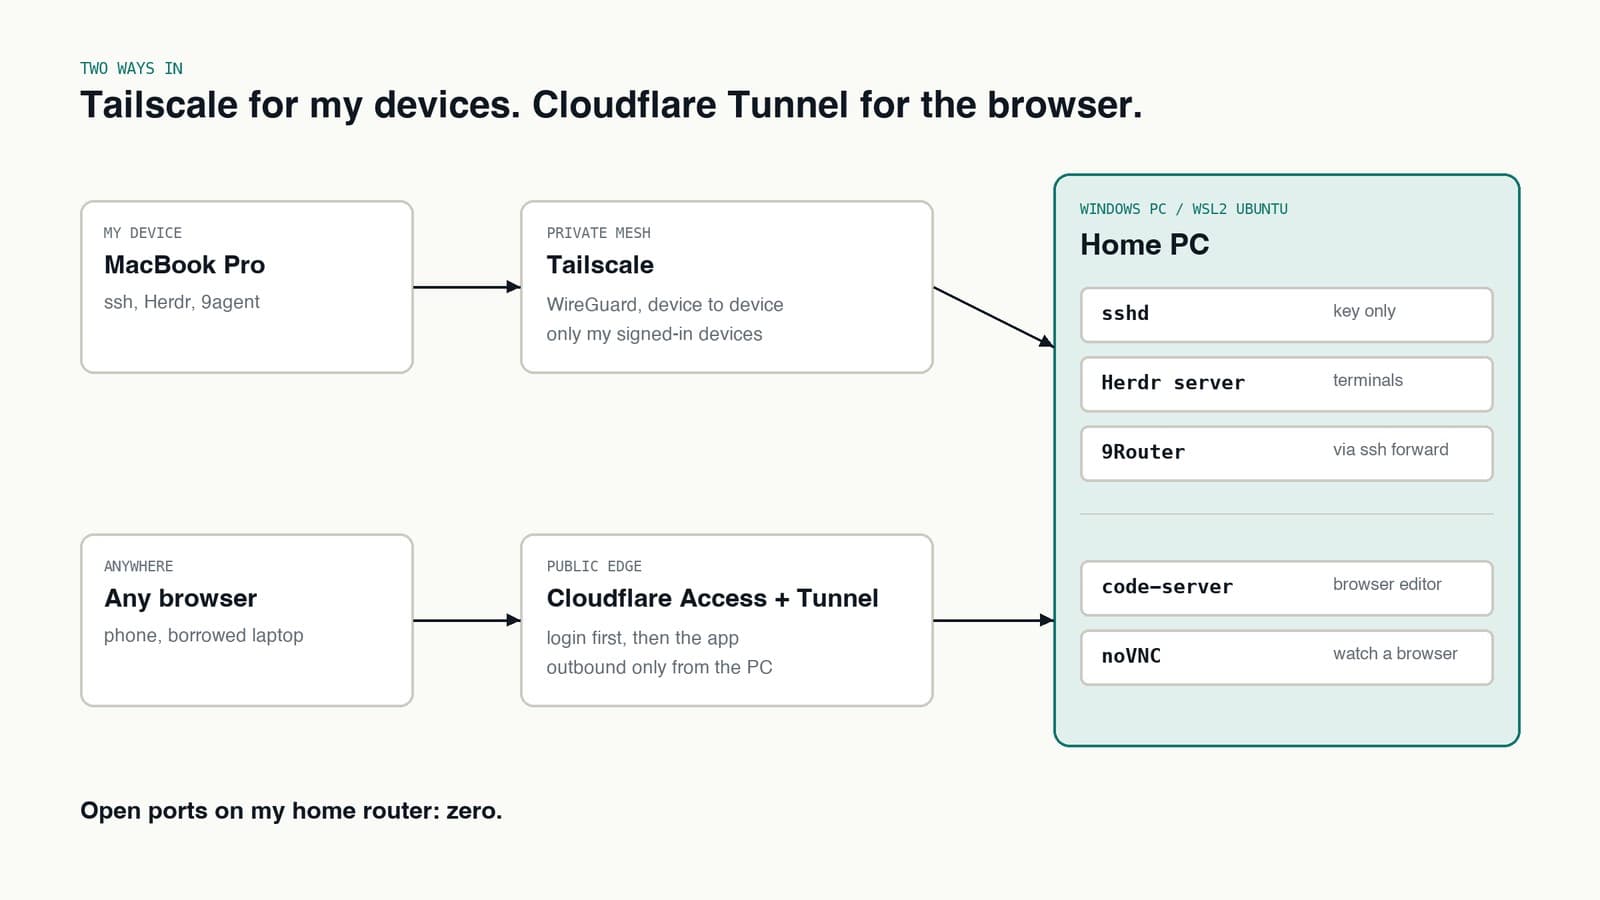
If it's interactive and powerful, it goes over Tailscale. If it's a web page I might open from a phone, it goes through Cloudflare with a login in front.
More on this: Tailscale, Cloudflare Tunnel and the things that bit me.
Herdr: my terminals on the PC, from the MacBook
Herdr is how the MacBook Pro gets into the PC. The Herdr server runs inside WSL2 Ubuntu on the Windows machine. The Herdr client runs on the MacBook and connects to it over ssh on Tailscale. I get the PC's Ubuntu terminals, split into panes and tabs, as if they were local.
Each task gets its own pane, usually in its own git worktree. The agents run in those panes on the PC, not on the MacBook.
Because the terminals live on the PC, closing the MacBook doesn't kill anything. I reconnect later, from the same MacBook or from somewhere else, and every pane is exactly where I left it.
More on this: how I use Herdr to reach the PC's terminals.
9Router: many accounts, one endpoint
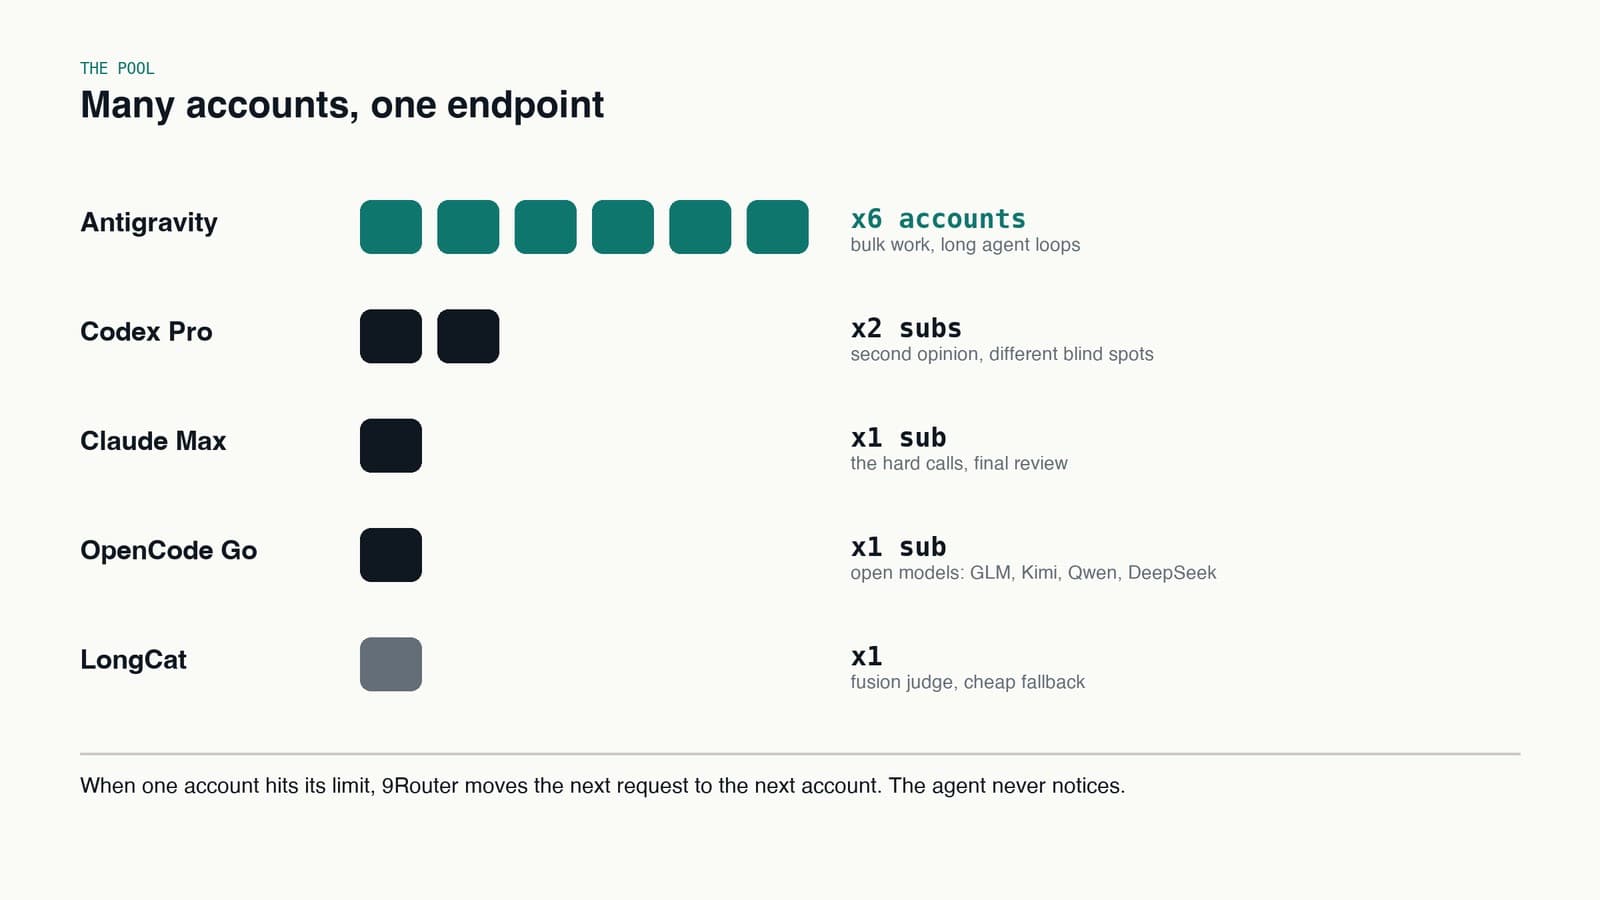
Every agent CLI I use (Claude Code, Codex, Pi, OpenCode) talks to one URL: localhost:20128/v1. That's 9Router, a self-hosted gateway that speaks the OpenAI-style API and fans out to real providers behind it.
Behind it sit:
- 6 Antigravity accounts for the bulk of the work and long agent loops
- 2 Codex Pro subscriptions for a second opinion with different blind spots
- 1 Claude Max subscription for the hard calls and final review
- OpenCode Go for open models (GLM, Kimi, Qwen, DeepSeek, MiniMax) on one flat subscription
- LongCat as a cheap fallback and as the judge in fusion combos
The agents never pick an account. They ask for a model name, which in 9Router is usually a combo: a named group of models with a strategy.
- Fallback: try the first model, and move to the next if it fails or is rate limited.
- Round robin: spread requests evenly across accounts.
- Fusion: send the same prompt to a small panel, then let a judge model pick or merge the best answer.
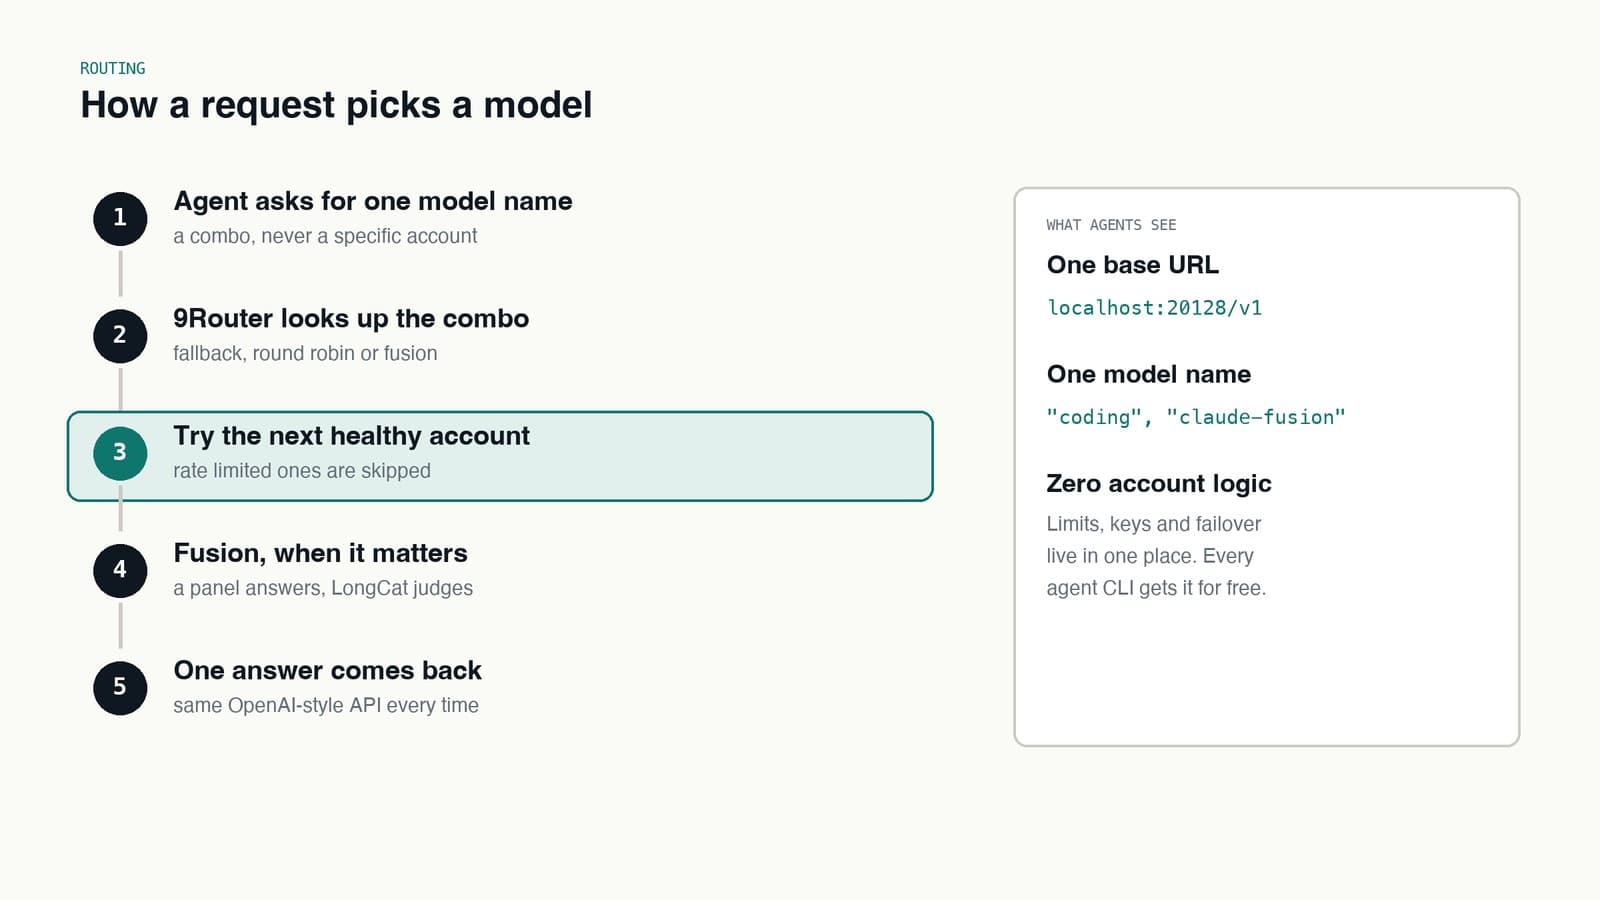
When one account hits its limit, 9Router moves the next request to the next account, and the agent never notices. Six Antigravity accounts means six chances before anything falls through to a paid fallback.
Account logic also lives in exactly one place. Keys, limits and failover are configured once. Every new agent CLI I try gets all of it by pointing at one URL.
More on this: 9Router, combos and keeping the model list fresh.
9agent: 9Router models inside Claude Code
Claude Code expects to talk to Anthropic. It doesn't have to. I wrote 9agent, a small launcher that reads the model list from 9Router, lets me pick an agent, a model and a permission mode, then starts the agent pointed at the gateway.
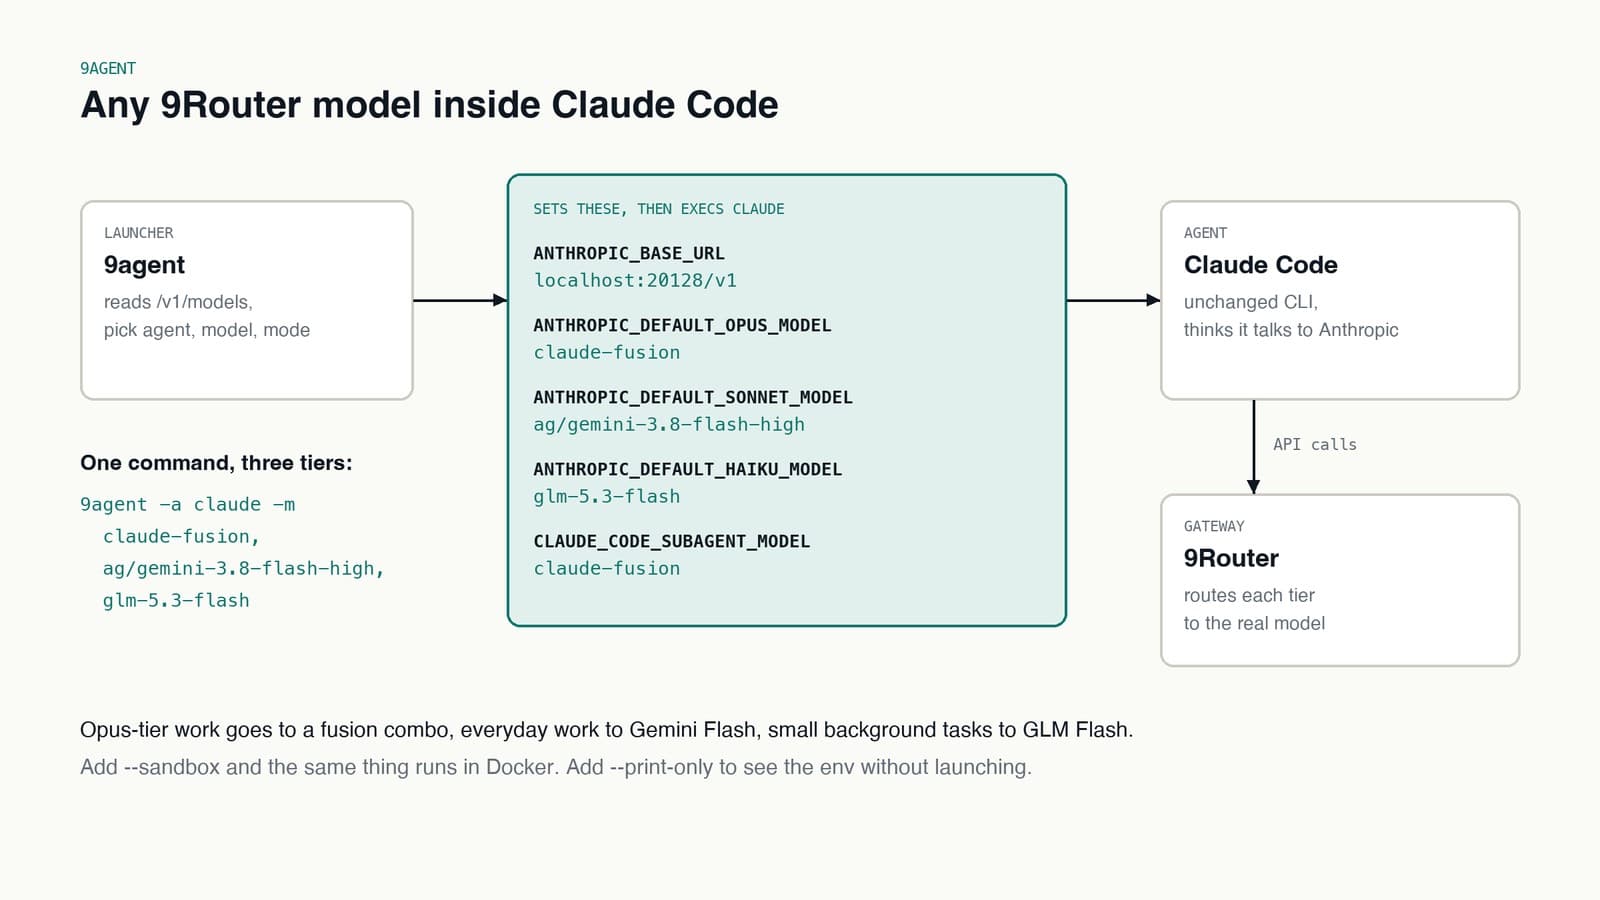
For Claude Code, it sets a handful of environment variables and gets out of the way:
9agent -a claude -m claude-fusion,ag/gemini-3.8-flash-high,glm-5.3-flash
ANTHROPIC_BASE_URL=http://localhost:20128/v1
ANTHROPIC_DEFAULT_OPUS_MODEL=claude-fusion
ANTHROPIC_DEFAULT_SONNET_MODEL=ag/gemini-3.8-flash-high
ANTHROPIC_DEFAULT_HAIKU_MODEL=glm-5.3-flash
CLAUDE_CODE_SUBAGENT_MODEL=claude-fusion
Claude Code still thinks it has an Opus, a Sonnet and a Haiku. Behind them, the heavy tier is a fusion combo, the everyday tier is Gemini Flash on the Antigravity pool, and the small background calls go to GLM Flash. Same CLI, same hooks, same skills, different models.
The flags I use constantly:
- No flags at all gives a searchable picker over everything 9Router serves.
--sandboxruns the same agent in Docker, with only the working directory and the agent's home mounted. It limits how much of the filesystem an agent can touch when I let it run unattended. It's a blast-radius limiter, not a security boundary: the container keeps full network access, because it needs it to reach the gateway (9agent sandbox docs).--print-onlyprints the resolved env and command without launching. Good for checking what an agent is about to talk to.-a pior-a hermeslaunches those agents against the same gateway instead.
9agent does one thing: resolve a model, exec the agent and pass its exit code back. It never rewrites my config files and never sits in the middle of the session.
More on this: 9agent, the sandbox and its two design rules.
Fusion models: when one answer isn't enough
Fusion is my favorite combo type. These are the ones I actually use:
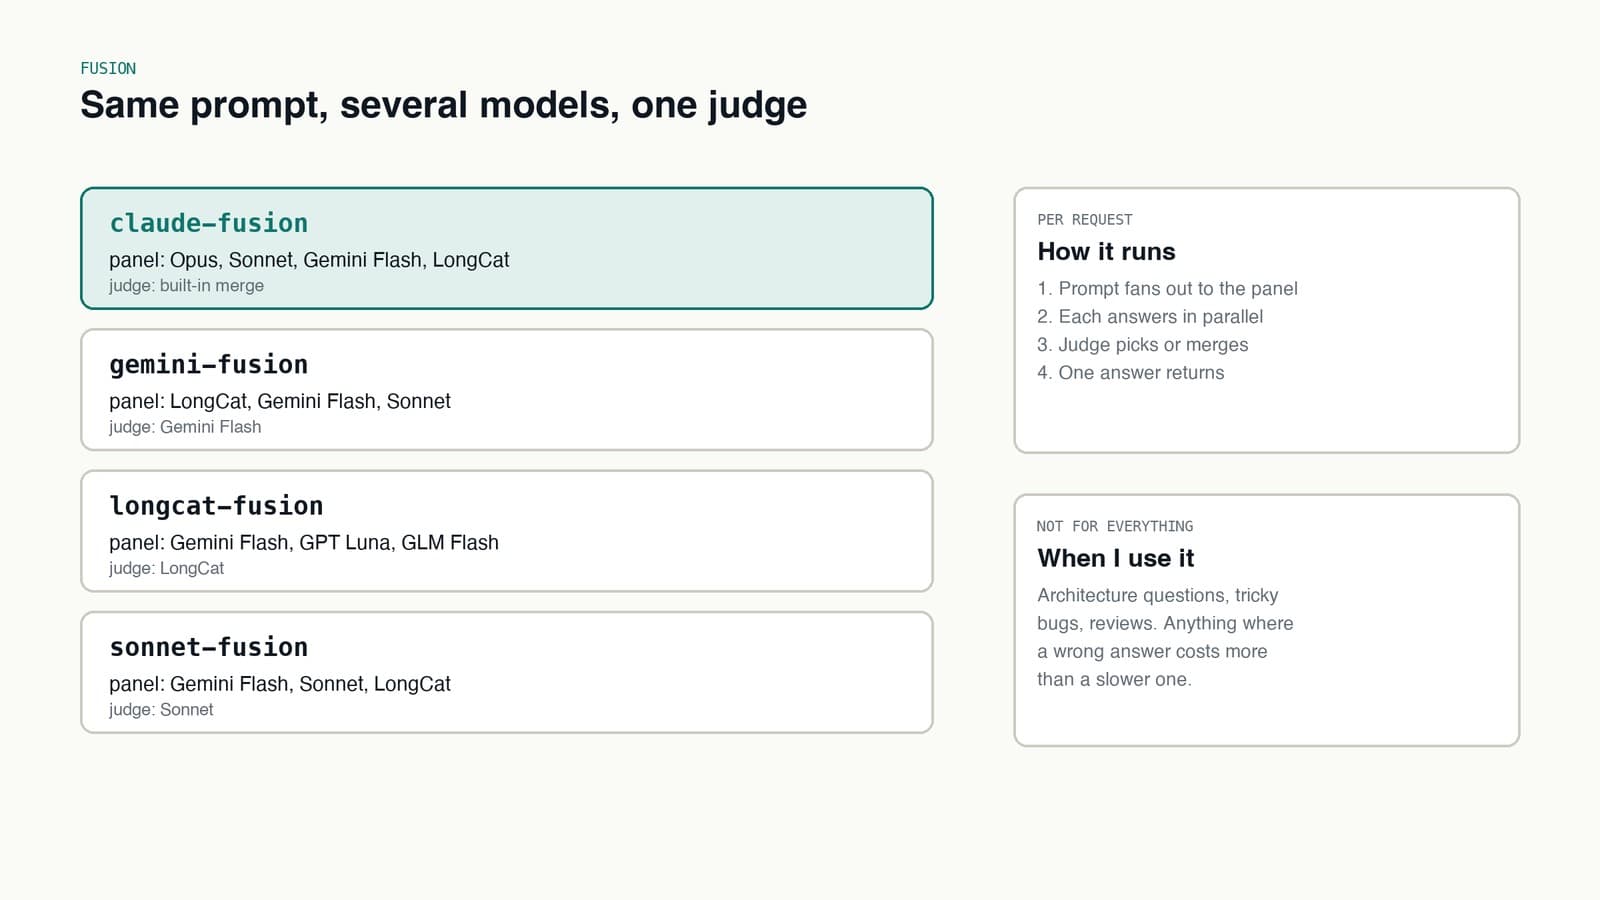
- claude-fusion: Opus, Sonnet, Gemini Flash and LongCat answer, then their answers get merged. My default for anything I would otherwise ask twice.
- gemini-fusion: LongCat, Gemini Flash and Sonnet, with Gemini Flash as judge. Fast and cheap.
- longcat-fusion: Gemini Flash, GPT Luna and GLM Flash, with LongCat as judge. Three model families, three sets of blind spots.
- sonnet-fusion: Gemini Flash, Sonnet and LongCat, with Sonnet as judge.
Fusion is slower and burns more quota, so it isn't the default. I reach for it on architecture questions, bugs that already fooled one model, and reviews. Anywhere a wrong answer costs more than a slow one.
Hermes: the agents that run when I'm not there
Interactive agents are half the setup. The other half is Hermes, an agent with a scheduler that runs jobs on its own.
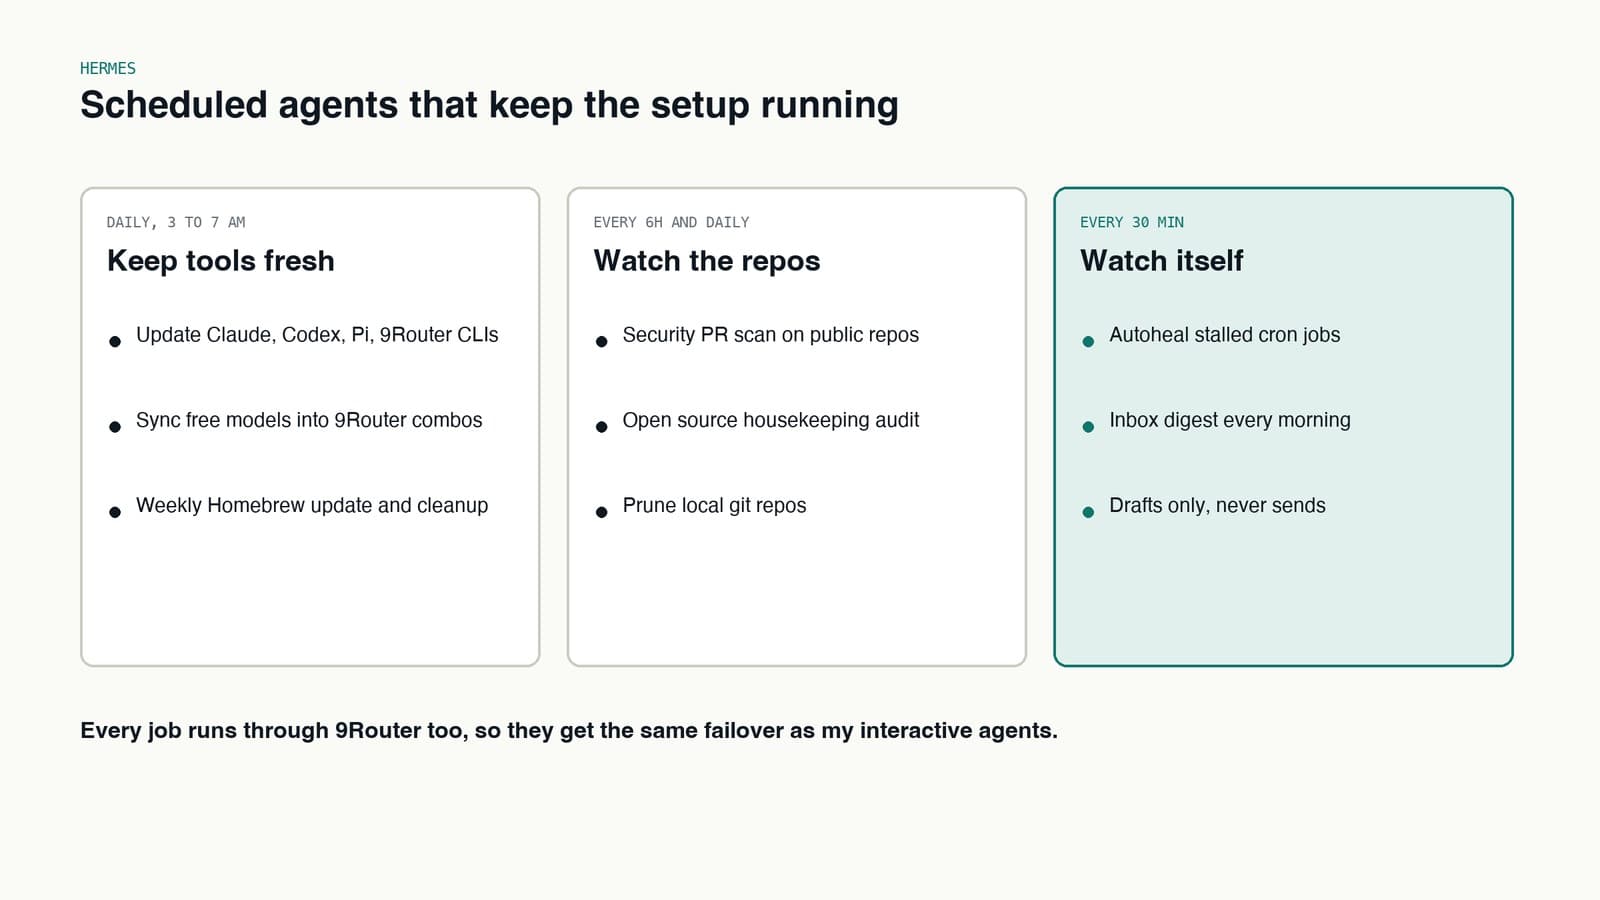
- Keep tools fresh. Every night it updates the Claude, Codex, Pi and 9Router CLIs, and syncs newly released free models into the right 9Router combos. I never wake up to a stale model list.
- Watch the repos. A security PR scan across my public repos every six hours, a daily open source housekeeping audit, and a nightly prune of local clones.
- Watch itself. An autoheal job checks every 30 minutes for scheduled jobs that stalled, and restarts them.
One rule covers all of it: Hermes drafts, and I send. It can message me, but it never sends anything to anyone else on my behalf.
More on this: Hermes jobs, skills, memory and the one rule.
Skills: small files that teach agents how I work
The other thing that compounds is skills. A skill is a short markdown file an agent loads when a task matches it: the steps, the commands, and the pitfalls I hit last time. When an agent gets something wrong and I correct it, the fix goes into the skill, where it outlives the chat.
The public ones worth stealing:
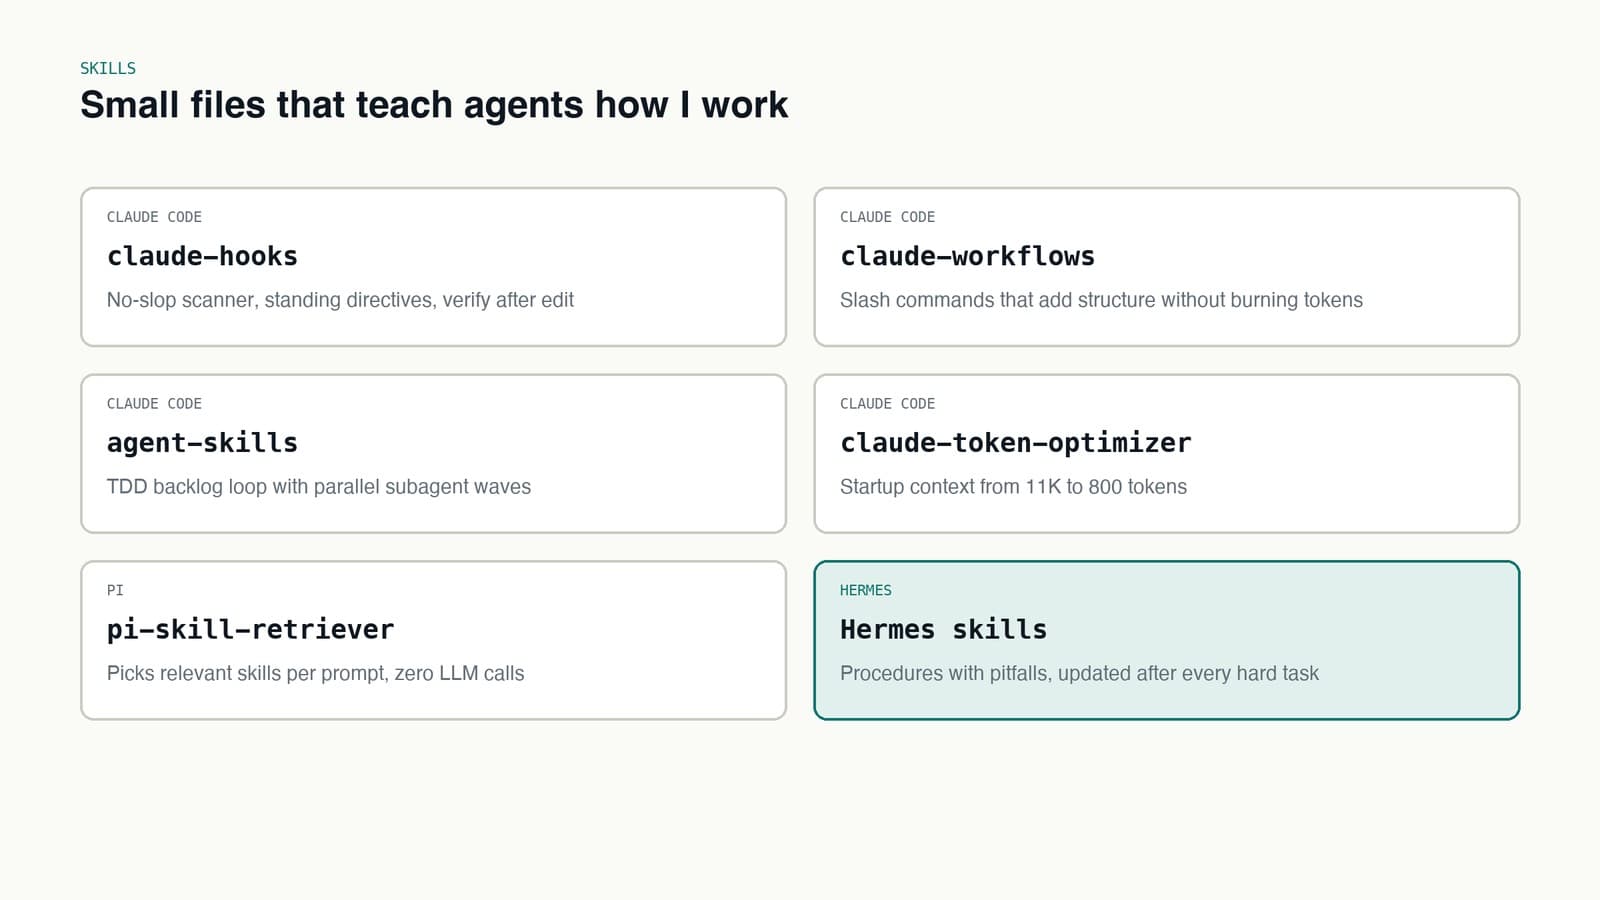
- claude-hooks: Claude Code hooks for standing engineering rules, a scanner that blocks AI filler, and a check after every edit.
- claude-workflows: slash commands that add structure to Claude Code without burning tokens.
- agent-skills: a TDD backlog loop that runs subagents in parallel waves.
- claude-token-optimizer: cuts Claude Code startup context from about 11K tokens to 800.
- pi-skill-retriever: picks relevant skills for each prompt in the Pi agent, with zero LLM calls.
My Hermes skills follow the same idea: one file per kind of task, each with a pitfalls section that grows every time something breaks. Those are the most valuable files on the machine.
Rebuild it in this order
If you want to copy this, build it from the bottom up. Each step leans on the one before it, so get one working before you add the next.
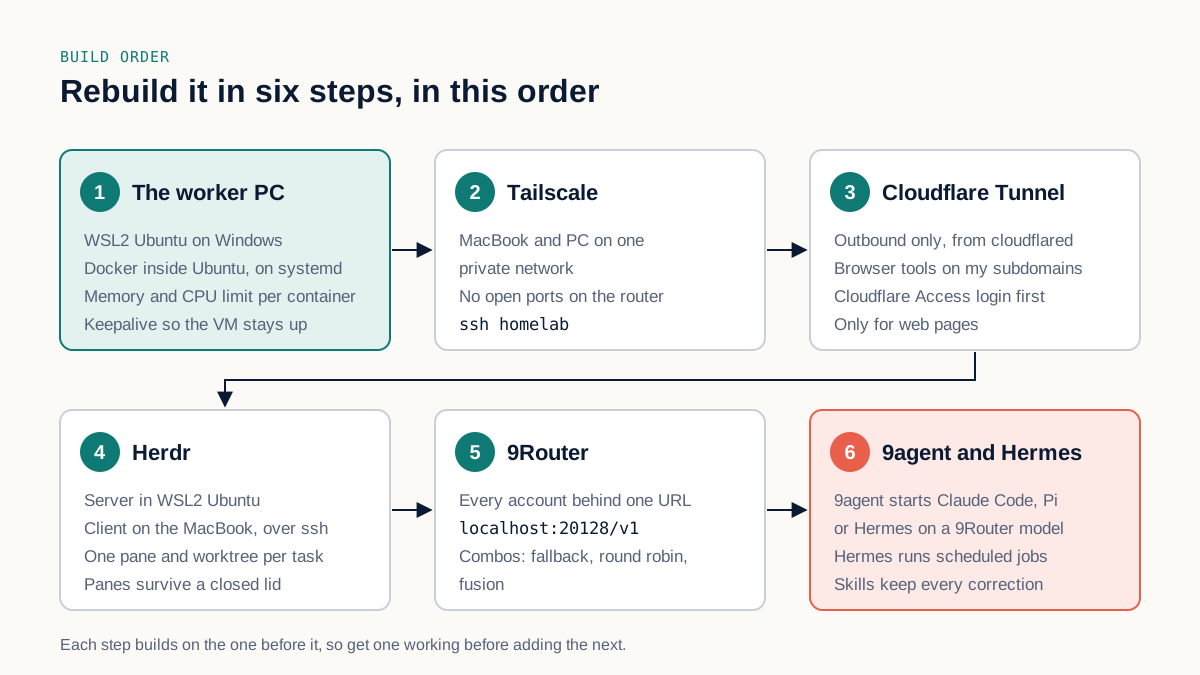
- Set up the worker PC. WSL2 Ubuntu, Docker inside Ubuntu under systemd, a memory and CPU limit on every container, and a keepalive on the Windows side.
- Join both machines to Tailscale. You're done when
ssh homelabworks from the MacBook, from anywhere, with no ports open on the router. - Add Cloudflare Tunnel, only for web pages. Put Cloudflare Access in front so every request needs a login before it reaches the PC. Keep ssh and anything powerful off it.
- Install Herdr. Server in WSL2 Ubuntu, client on the MacBook over ssh. Close the lid, reopen it and check your panes are still there.
- Put 9Router in front of your accounts. Point every agent CLI at
localhost:20128/v1and set up combos for fallback, round robin and fusion. - Add 9agent and Hermes. 9agent to launch Claude Code, Pi or Hermes on any 9Router model. Hermes for the nightly updates, repo watching and autoheal, plus the skills that hold your corrections.
Gotchas worth knowing before you start
- WSL2 shuts down when nothing is attached. Windows shuts the Ubuntu VM down, and every service vanishes with it. A small keepalive on the Windows side fixes that.
- The tunnel is for web pages, not shells. Interactive, powerful access stays on Tailscale. Anything through Cloudflare gets an Access login in front of it.
--sandboxlimits blast radius, not exfiltration. It narrows what files an agent can touch, but the container still has network access.- Fusion is slow and quota-hungry. Save it for questions where a wrong answer costs more than a slow one.
What a day looks like
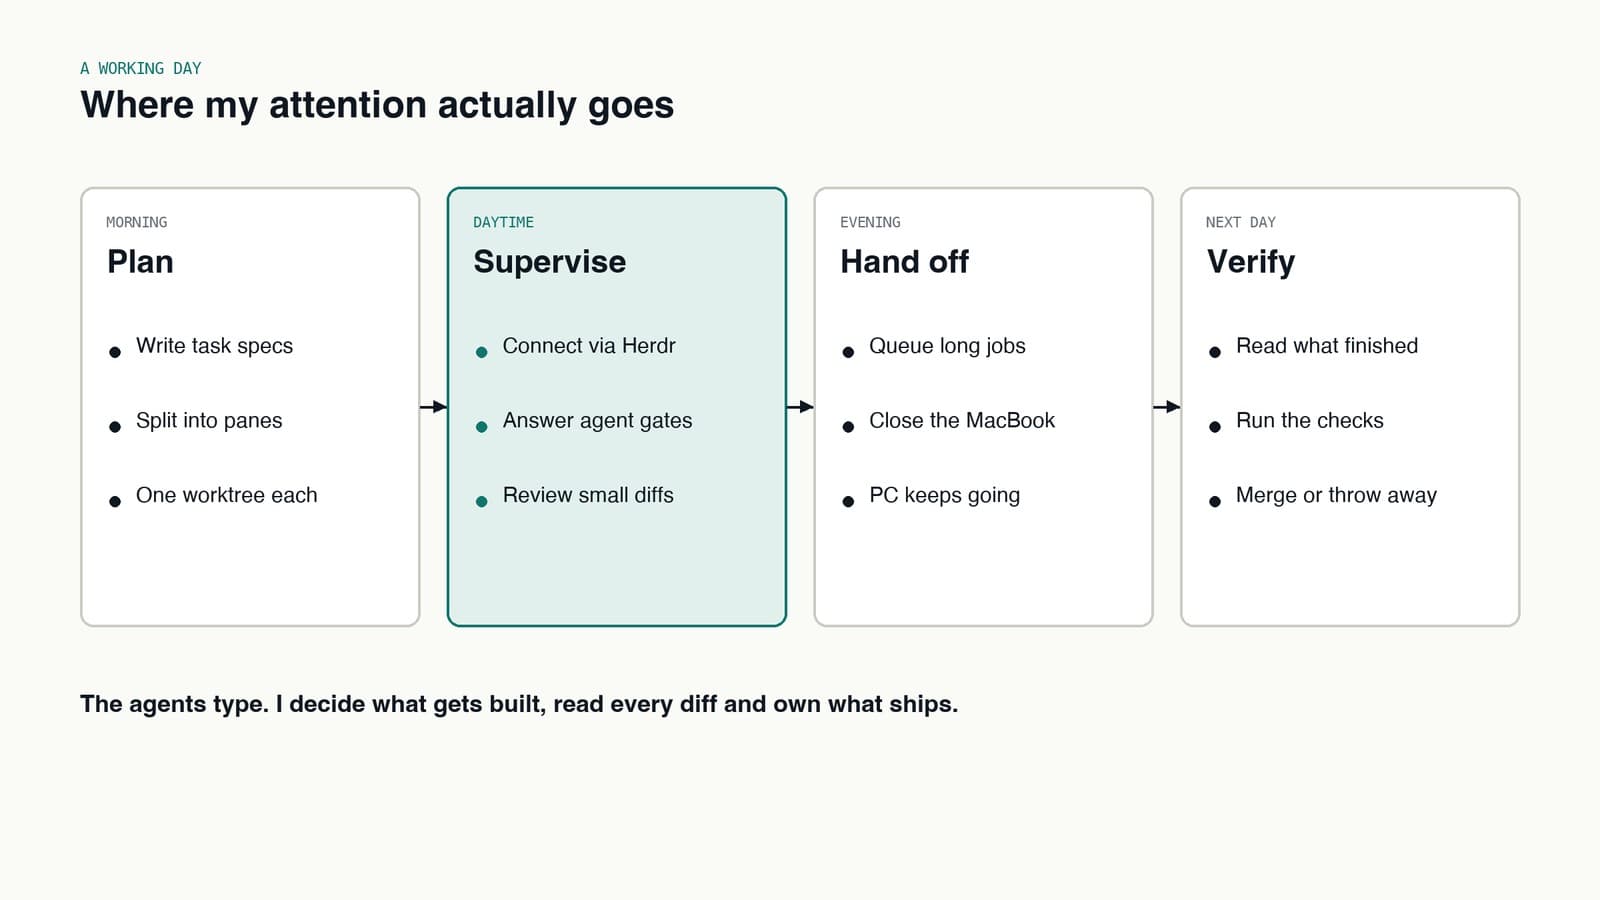
- Plan. Write short task specs. One pane and one worktree per task.
- Supervise. Connect through Herdr, answer what needs me, and review small diffs as they land.
- Hand off. Queue the long jobs in the evening and close the MacBook. The PC keeps going.
- Verify. Next morning, read what finished, run the checks, then merge it or throw it away.
The agents do the typing. I decide what gets built, read every diff and own what ships, all from the MacBook. The setup just makes sure the typing never waits on its lid being open.
Takeaways for anyone copying this
- Separate where you type from where work runs. That one change removed most of my interruptions.
- Don't open ports. A private mesh for your devices and a tunnel with a login for the browser is less work than hardening an exposed box.
- Put a gateway in front of your models early. Once more than one tool and more than one account are involved, routing in each tool separately becomes a mess.
- Keep the terminals where the work is. If the sessions live on the machine doing the work, any device that can connect is a full workstation.
- Write the lesson down where the agent will read it. A correction in chat is gone tomorrow. A correction in a skill is there forever.
Related posts
- 9Router: one local endpoint in front of every AI coding account I have
9Router puts 6 Antigravity, 2 Codex Pro, Claude Max and other accounts behind one localhost endpoint. Fallback, round robin and fusion combos hide rate limits.
- Go berserk: one night with Grok Bot, Orca and every gate still on
My Grok Bot usage reset, so I told my AI teammates to go berserk overnight. They set up Orca, fixed a Windows PC and refreshed my blog, and every order kept the review gates on.
- Tailscale and Cloudflare Tunnel: my home PC with zero open ports
How I reach my home PC: Tailscale for ssh and Herdr from my own devices, Cloudflare Tunnel with Access for browser tools, and no open router ports.