- Published on
My CI/CD pipeline: Husky hooks, GitHub Actions, Trivy and Vercel
- Authors

- Name
- Nadim Tuhin
- @nadimtuhin
On this page
Six months ago, I was building and deploying every project by hand.
Now I push code, grab a coffee, and watch automated tests, security scans and deployments run in parallel. Nothing ships until every check is green.
Here's the complete workflow I've refined across 60+ open-source projects, stage by stage.
TL;DR: the workflow
| Stage | Tool | What Happens |
|---|---|---|
| Commit | Git | Pre-commit hooks run linters |
| Push | GitHub Actions | Matrix tests + security scan |
| PR | Claude AI | Automated code review |
| Merge | Vercel | Zero-downtime deployment |
| Monitor | Trivy/GitHub | Vulnerability alerts |
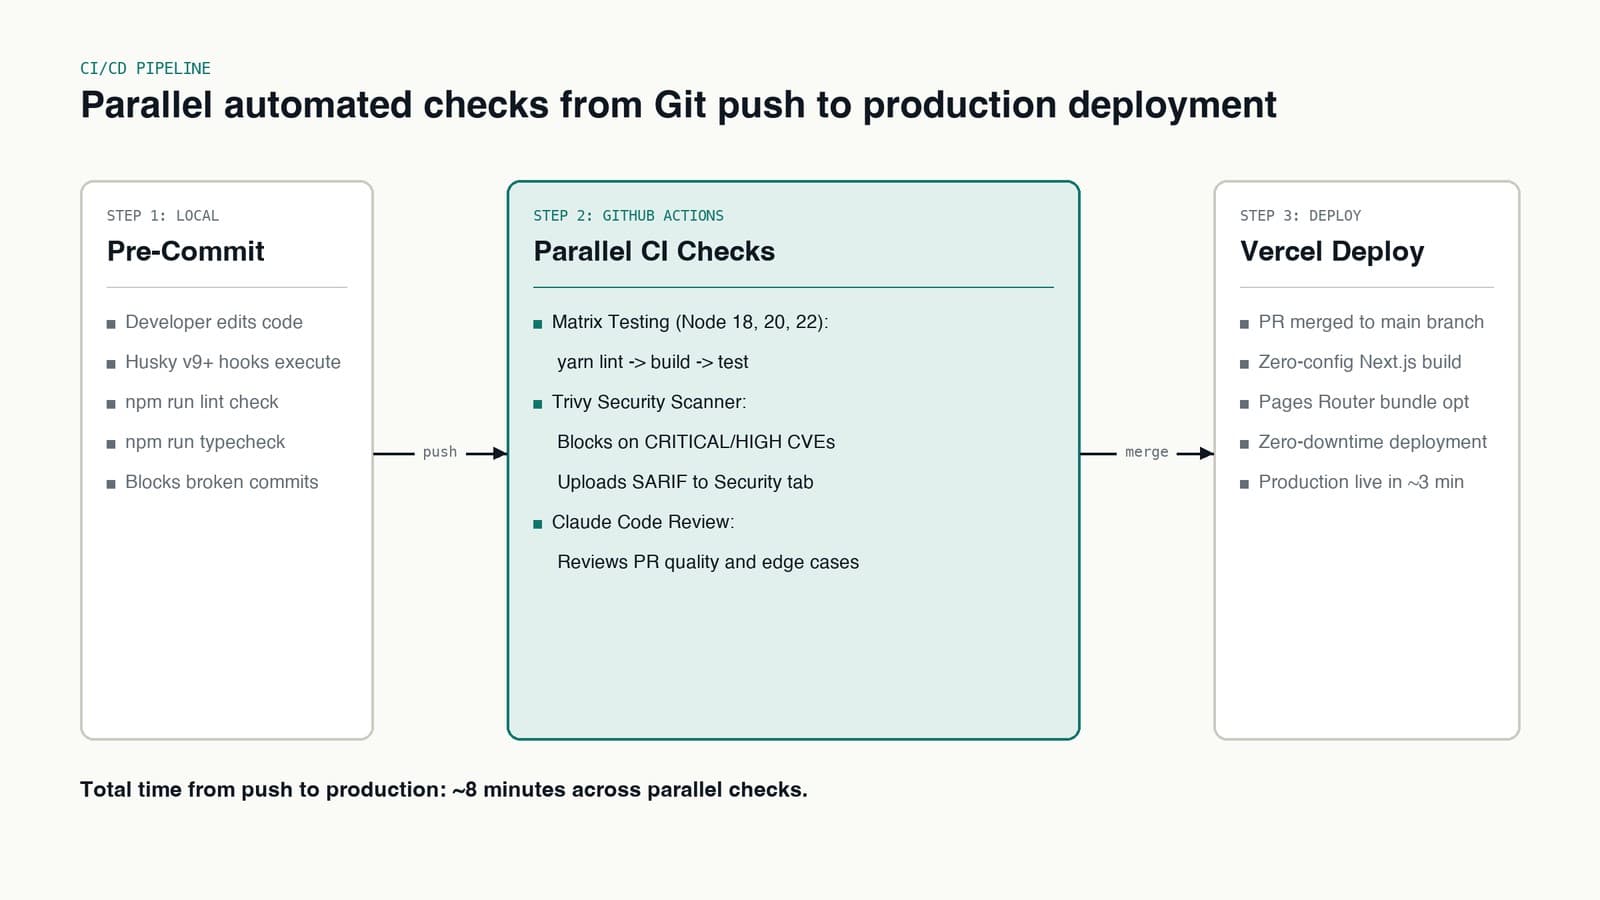
Total time from push to production: ~11 minutes (about 8 for tests, security scan and review, then about 3 for the Vercel deploy).
Pipeline overview
Local development
- Code Change -> Developer makes changes
- Husky Pre-commit Hooks -> Runs lint and typecheck
- Commit -> If hooks pass, commit succeeds
GitHub Actions (triggered on push)
| Job | Description | Runs |
|---|---|---|
| Matrix Testing | Tests across Node 18, 20, 22 | Parallel |
| Security Scan (Trivy) | Blocks PR on CRITICAL/HIGH | Parallel |
| Claude AI Code Review | Reviews code quality & security | Parallel |
Matrix Testing Flow: lint -> build -> test (sequential within each Node version)
Deployment (after all checks pass)
- PR Merge -> All checks must pass
- Vercel Deployment -> Build + optimize + zero-downtime deploy
- Production Live -> Site is updated
The Git workflow
Branch strategy
After years of experimenting, I settled on something simple:
# Main branches
main           # Production-ready code
develop         # Development integration

# Feature branches
feature/project-name
fix/bug-description
hotfix/urgent-fix
Rules:
- Never push directly to
main - All changes go through pull requests
mainis always deployabledevelopmerges tomainvia PR
Commit convention
I use Conventional Commits for automation:
# Format: <type>(<scope>): <description>
feat(auth): add OAuth2 login flow
fix(api): resolve rate limiting bug
docs(readme): update installation steps
test(auth): add user session tests
security(api): sanitize SQL queries
Why it matters: Git hooks and CI can parse commit types and skip checks they don't need.
Pre-Commit Automation
Husky v9+ runs linting before I can commit:
# Install and set up Husky
npm install husky --save-dev
npx husky init

# Create pre-commit hook
echo "npm run lint && npm run typecheck" > .husky/pre-commit
The .husky/pre-commit file runs on every commit. If linting fails, the commit is blocked, so broken code never lands in the repository.
CI/CD Pipeline
GitHub Actions Matrix Testing
Every push triggers matrix builds across Node versions:
# .github/workflows/ci.yml
name: CI

on:
  push:
    branches: [main, develop]
  pull_request:
    branches: [main, develop]

jobs:
  test:
    runs-on: ubuntu-latest
    strategy:
      fail-fast: false
      matrix:
        node-version: [18.x, 20.x, 22.x]

    steps:
      - uses: actions/checkout@v3
      - name: Use Node.js ${{ matrix.node-version }}
        uses: actions/setup-node@v3
        with:
          node-version: ${{ matrix.node-version }}
          cache: 'yarn'

      - name: Install dependencies
        run: yarn install --frozen-lockfile

      - name: Run linter
        run: yarn lint

      - name: Build project
        run: yarn build

      - name: Run tests
        run: yarn test
Benefits:
- Tests against multiple Node versions (18 LTS, 20 LTS, 22 Current)
- Catches version-specific bugs before deployment
- Runs in parallel (all versions simultaneously, depends on runner availability)
fail-fast: falseensures all versions are tested even if one fails
Automated security scanning
Trivy scans on every push and PR:
# .github/workflows/security-scan.yml
name: Security Scan

on:
  push:
    branches: [main, develop]
  pull_request:
    branches: [main, develop]
  schedule:
    # Run weekly on Sundays at 2 AM UTC
    - cron: '0 2 * * 0'

jobs:
  trivy:
    name: Trivy vulnerability scanner
    runs-on: ubuntu-latest
    permissions:
      contents: read
      pull-requests: write
      security-events: write

    steps:
      - name: Checkout code
        uses: actions/checkout@v4

      - name: Run Trivy vulnerability scanner
        uses: aquasecurity/trivy-action@master
        with:
          scan-type: 'fs'
          scan-ref: '.'
          format: 'sarif'
          output: 'trivy-results.sarif'
          severity: 'CRITICAL,HIGH'

      - name: Upload Trivy scan results to GitHub Security tab
        uses: github/codeql-action/upload-sarif@v3
        if: always()
        with:
          sarif_file: 'trivy-results.sarif'
          category: 'Trivy'

      - name: Comment PR on failure
        if: failure() && github.event_name == 'pull_request'
        uses: actions/github-script@v7
        with:
          script: |
            github.rest.issues.createComment({
              issue_number: context.issue.number,
              owner: context.repo.owner,
              repo: context.repo.repo,
              body: `⚠️ Security vulnerabilities detected! Please review the [Security tab](https://github.com/${context.repo.owner}/${context.repo.repo}/security/code-scanning) for details.`
            })
One catch: trivy-action exits 0 by default, even when it finds vulnerabilities. To make CRITICAL and HIGH findings fail the job (and so block the PR and fire the comment step), add exit-code: '1' to the scan step's with: block.
Key features:
- Scan triggers: Push, PR, weekly schedule
- Severity threshold: Only blocks on CRITICAL/HIGH
- SARIF upload: Vulnerabilities appear in GitHub Security tab
- PR comments: Automatic alerts when vulnerabilities detected
- Weekly scans: Catch new CVEs even without code changes
AI-Powered Code Review
Claude Code Review runs on every PR:
# .github/workflows/claude-code-review.yml
name: Claude Code Review

on:
  pull_request:
    types: [opened, synchronize]

jobs:
  claude-review:
    runs-on: ubuntu-latest
    permissions:
      contents: read
      pull-requests: read
      issues: read
      id-token: write

    steps:
      - name: Checkout repository
        uses: actions/checkout@v4
        with:
          fetch-depth: 1

      - name: Run Claude Code Review
        uses: anthropics/claude-code-action@beta
        with:
          claude_code_oauth_token: ${{ secrets.CLAUDE_CODE_OAUTH_TOKEN }}
          direct_prompt: |
            Please review this pull request and provide feedback on:
            - Code quality and best practices
            - Potential bugs or issues
            - Performance considerations
            - Security concerns
            - Test coverage

            Be constructive and helpful in your feedback.
What Claude catches:
- Logic errors I missed
- Security vulnerabilities
- Performance bottlenecks
- Missing edge cases
- Test coverage gaps
Real example: Claude once caught a potential SQL injection in a helper function that 3 manual reviewers missed.
Deployment strategy
Next.js on Vercel
Most of my projects deploy to Vercel. For Next.js, Vercel requires zero configuration - it auto-detects and optimizes your app. No vercel.json needed for standard deployments.
Build optimization (Pages Router only):
// next.config.js
module.exports = {
  reactStrictMode: true,

  // Use Preact in production for smaller bundle
  webpack: (config, { dev, isServer }) => {
    if (!dev && !isServer) {
      Object.assign(config.resolve.alias, {
        react: 'preact/compat',
        'react-dom': 'preact/compat',
      })
    }

    return config
  },
}
Result: Smaller first load JS compared to full React.
Caveat: This Preact swap only works with the Pages Router. It will break React Server Components, Suspense, and the App Router (Next.js 13+). For App Router projects, skip this optimization - React 18's tree-shaking is already efficient.
Security headers
Next.js applies security headers via configuration:
// next.config.js
const securityHeaders = [
  {
    key: 'Content-Security-Policy',
    value:
      'default-src "self"; script-src "self" "unsafe-eval" giscus.app analytics.ahrefs.com; style-src "self" "unsafe-inline" cdn.jsdelivr.net; img-src * data:;',
  },
  {
    key: 'Strict-Transport-Security',
    value: 'max-age=31536000; includeSubDomains; preload',
  },
  {
    key: 'X-Frame-Options',
    value: 'DENY',
  },
  {
    key: 'X-Content-Type-Options',
    value: 'nosniff',
  },
]

module.exports = {
  async headers() {
    return [
      {
        source: '/(.*)',
        headers: securityHeaders,
      },
    ]
  },
}
One fix if you copy this: CSP keywords need single quotes inside the header value ('self', 'unsafe-eval', 'unsafe-inline'). Browsers don't treat the double-quoted "self" above as a keyword.
Headers applied:
- CSP: Prevents XSS attacks
- HSTS: Forces HTTPS for 1 year
- X-Frame-Options: Blocks clickjacking
- X-Content-Type-Options: Stops MIME sniffing attacks
Docker deployment
For backend services, I use Docker:
# Dockerfile for Node.js service
FROM node:18-alpine
WORKDIR /app
# Install ALL dependencies (including devDependencies for build)
COPY package*.json ./
RUN npm ci
# Copy source with correct ownership
COPY . .
# Build the project
RUN npm run build
# Remove devDependencies after build
RUN npm prune --production
# Expose port
EXPOSE 3000
# Non-root user for security
USER node
CMD ["npm", "start"]
Docker Compose for local development:
# docker-compose.yml
services:
  app:
    build: .
    ports:
      - '3000:3000'
    environment:
      - NODE_ENV=development
      - DATABASE_URL=${DATABASE_URL}
    depends_on:
      - db

  db:
    image: postgres:15-alpine
    environment:
      - POSTGRES_PASSWORD=${DB_PASSWORD}
    volumes:
      - postgres_data:/var/lib/postgresql/data

volumes:
  postgres_data:
Benefits:
- Consistent environments (local = staging = production)
- Easy scaling with Docker Swarm/Kubernetes
- Volume persistence for databases
- One command to start entire stack
Monitoring and Maintenance
GitHub Security Tab Integration
All Trivy scans upload SARIF results to GitHub Security:
- name: Upload Trivy scan results to GitHub Security tab
  uses: github/codeql-action/upload-sarif@v3
  if: always()
  with:
    sarif_file: 'trivy-results.sarif'
    category: 'Trivy'
Result:
- Vulnerability dashboard at
/security - Alerts for new CVEs
- Integration with Dependabot
- Historical tracking of security issues
Automated dependency updates
I use Renovate or Dependabot:
// renovate.json
{
  "extends": ["config:base"],
  "schedule": ["every weekend"],
  "automerge": false,
  "prConcurrentLimit": 5,
  "labels": ["dependencies"]
}
What it does:
- Scans
package.jsonfor outdated dependencies - Opens PRs with version updates
- Groups related updates (e.g., all React packages)
- Respects semantic versioning (major vs minor vs patch)
Rules:
- Patch and minor updates: Create PRs for review
- Major updates: Notify via issue (requires manual review)
- Security vulnerabilities: Immediate alert
Error tracking
For production apps, I integrate error tracking:
// Error boundary example
class ErrorBoundary extends React.Component {
  state = { hasError: false, error: null }

  static getDerivedStateFromError(error) {
    return { hasError: true, error }
  }

  componentDidCatch(error, errorInfo) {
    // Log to error tracking service
    logError({
      error: error.toString(),
      stack: error.stack,
      componentStack: errorInfo.componentStack,
      userAgent: navigator.userAgent,
      url: window.location.href,
      timestamp: new Date().toISOString(),
    })
  }

  render() {
    if (this.state.hasError) {
      return <div>Something went wrong. Please refresh the page.</div>
    }
    return this.props.children
  }
}
Benefits:
- Real-time error alerts
- User context (browser, URL, timestamp)
- Stack traces for debugging
- Grouping similar errors (don't spam notifications)
Complete workflow example
Scenario: Fixing a Bug
# 1. Create feature branch
git checkout -b fix/login-timeout

# 2. Make changes
# ... edit code ...

# 3. Pre-commit hooks run
git add .
git commit -m "fix(auth): resolve session timeout issue"
# -> Husky runs: npm run lint && npm run typecheck

# 4. Push to remote
git push origin fix/login-timeout

# 5. Open PR on GitHub
# -> Automatically triggers:
#   • Matrix tests (Node 18, 20, 22)
#   • Trivy security scan
#   • Claude code review

# 6. Review feedback
# -> Claude comments: "Potential race condition in line 42"
# -> Security scan: "No vulnerabilities found"

# 7. Fix feedback
# ... edit code ...
git commit -m "fix(auth): address race condition in session check"
git push

# 8. CI passes, merge to main
# -> Triggers Vercel deployment

# 9. Production deployment
# -> Vercel builds and deploys in ~3 minutes
# -> Zero downtime with preview deployments

# 10. Monitor
# -> Error tracking confirms fix resolved
# -> Security tab shows no new vulnerabilities
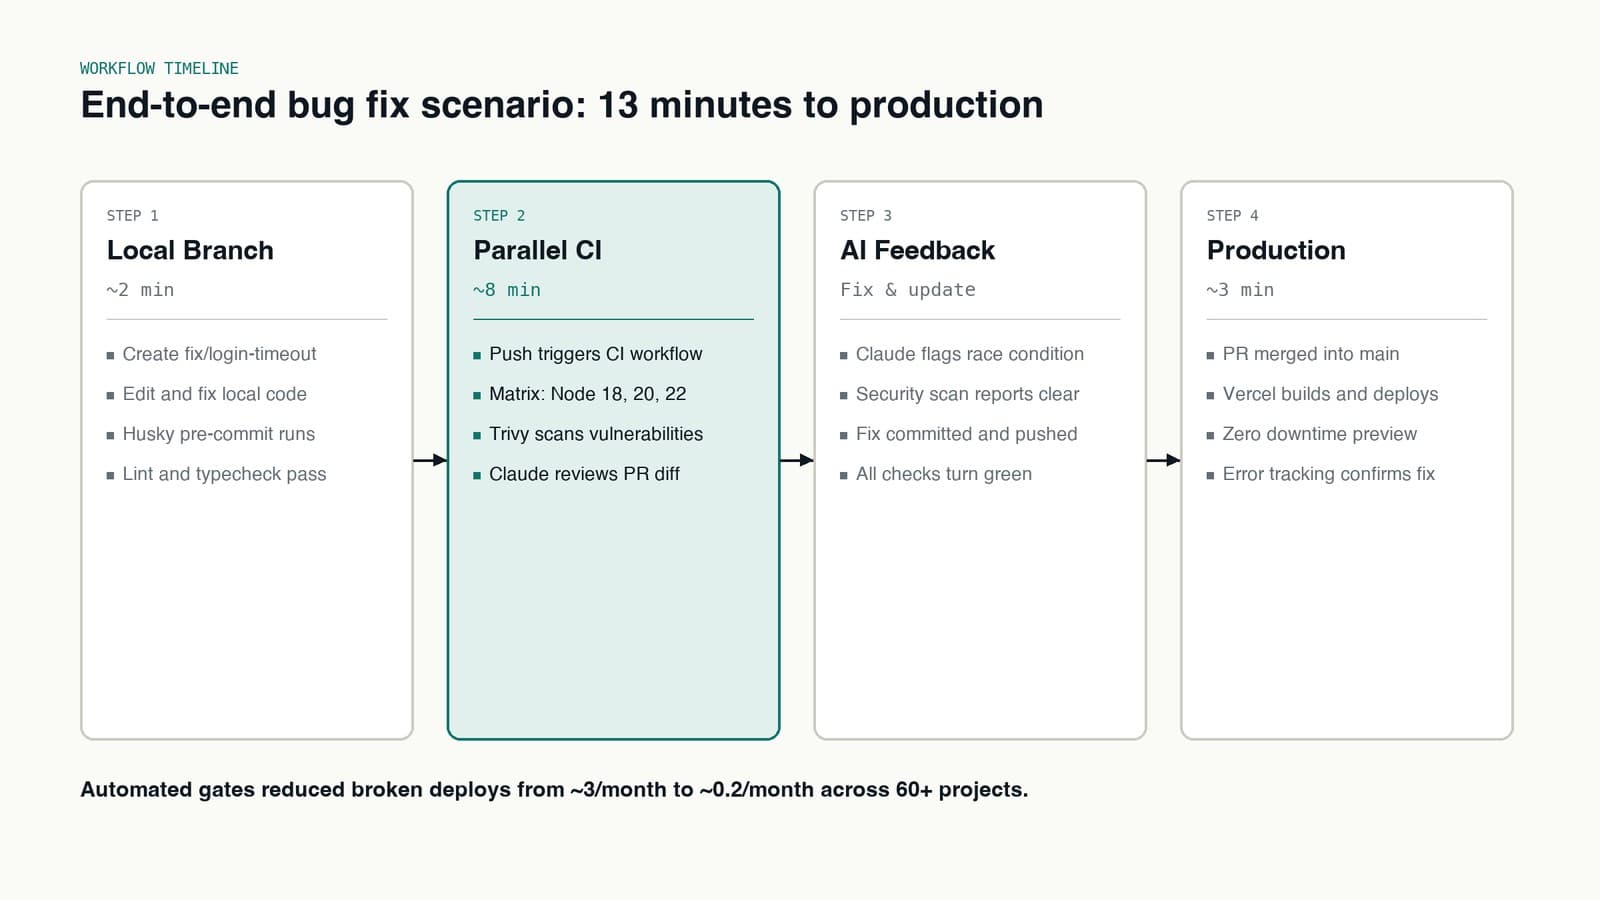
Total time:
- Initial commit: ~2 minutes
- CI/CD: ~8 minutes (tests + scan + review)
- Deployment: ~3 minutes
- Total: ~13 minutes from local fix to production
Performance metrics
After implementing this workflow across projects:
| Metric | Before | After |
|---|---|---|
| Deploy time | 30-45 minutes (manual) | 3 minutes (automated) |
| Broken deploys | ~3/month (forgot to test) | ~0.2/month (CI blocked) |
| Security scan frequency | Never (too busy) | Every push + weekly |
| Code review coverage | 60% (human fatigue) | 100% (AI + human) |
| Deployment anxiety | High (manual process) | Low (automated gates) |
Tool stack
| Tool | Purpose | Why I chose it |
|---|---|---|
| Git | Version control | Industry standard |
| GitHub Actions | CI/CD | Free, fast, great UI |
| Trivy | Security scanning | Vulnerability scans, SARIF support |
| Claude Code Review | Automated PR review | Catches issues humans miss |
| Vercel | Next.js deployment | Zero-config, fast, free |
| Docker | Containerization | Portable, scalable |
| Husky | Pre-commit hooks | Prevents broken commits |
| Renovate | Dependency updates | Better than Dependabot |
| Preact | Bundle optimization | Smaller bundle (Pages Router only) |
Cost analysis
Monthly costs for DevOps stack
| Service | Cost | What it provides |
|---|---|---|
| GitHub Actions | $0 (2000 free minutes/month) | CI/CD, security scans |
| Vercel Pro | $20/month | Faster builds, analytics |
| Domain (nadimtuhin.com) | $12/year | Custom domain |
| Email hosting | $5/month | Transactional emails |
| Monitoring (optional) | $0-10/month | Error tracking (Sentry/Honeybadger) |
| Total | ~$25-30/month | Complete DevOps pipeline |
When this workflow won't work
This setup assumes:
- GitHub-hosted code: If you use GitLab/Bitbucket, use GitLab CI/Jenkins
- Next.js projects: Other frameworks need different deployment (Netlify, Heroku, etc.)
- Small-to-medium teams: Large enterprises might need specialized tools
- Standard stack: If you use monorepos with multiple languages, complexity increases
Alternatives:
- GitLab CI: Similar to GitHub Actions, built into GitLab
- Jenkins: Highly customizable, but complex setup
- CircleCI: Great for Docker-heavy workflows
- Netlify: Simpler than Vercel, but fewer features
Future improvements
What's Working Well
- Trivy blocks deploys with CRITICAL or HIGH vulnerabilities
- Claude reviews every pull request
- Every branch gets a Vercel preview deployment
- Tests run on Node 18, 20 and 22
What needs improvement
- Canary deployments: Roll out to 10% of users, monitor, then full rollout
- Feature flags: Launch features behind flags instead of deployments
- Performance monitoring: Add APM (Application Performance Monitoring)
- Rollback automation: One-click rollback on error spikes
Planned changes
Canary deployment strategy:
# Future workflow
- name: Deploy canary
  run: |
    # Deploy to 10% of traffic
    kubectl patch deployment -p '{"spec":{"replicas":1}}'
    wait 10 minutes
    check_error_rate()
    if error_rate > threshold:
      rollback()
    else:
      full_rollout()
Lessons learned
1. Start Simple, Expand Based on Need
I didn't implement everything at once. Started with:
- Basic CI (build + test)
- Added security scanning
- Added automated code review
- Optimized deployment
Each addition solved a specific pain point.
2. Automation Pays for Itself Quickly
First week after setting up automated tests, I prevented 3 broken deployments. The setup time was recovered in 2 days.
3. Security Can't Be an Afterthought
Adding Trivy scanning took 2 hours. It caught a critical vulnerability in a dependency that would have exposed user data.
4. Documentation Is Critical
I document every workflow change in README files. When I revisit projects months later, context is already there.
5. Metrics Drive Decisions
I track:
- CI/CD success rates
- Deployment frequency
- Time from commit to production
- Security scan results
- Error rates post-deployment
These metrics tell me what to improve next.
Getting started
If you want to adopt this workflow:
Step 1: Add GitHub Actions CI
# Create .github/workflows/ci.yml
# Copy matrix testing workflow from above
Step 2: Add Security Scanning
# Create .github/workflows/security-scan.yml
# Copy Trivy workflow from above
Step 3: Connect to Vercel
npm install -g vercel
vercel login
vercel link
Step 4: Add Pre-commit Hooks
npm install husky lint-staged --save-dev
npx husky install
npx husky add .husky/pre-commit "npx lint-staged"
If you're on Husky v9 or later, husky add no longer works (it prints a deprecation message and exits). Use npx husky init and write the hook file directly, as in the pre-commit section above.
Step 5: Test the Full Pipeline
# Create a test branch
git checkout -b test-pipeline

# Make a trivial change
echo "test" > test.txt
git add test.txt
git commit -m "test(ci): verify pipeline"

# Push and watch everything run
git push origin test-pipeline
Confidence over ceremony
The real takeaway: a fast pipeline changes how you ship code. When local hooks and CI run on every push, you stop skipping tests or putting security scans off until staging.
Automated tests catch regressions before users see them. Dependency vulnerability scans block known exploits before code merges to main.
Resources
Frequently asked questions
- What does a zero-touch CI/CD pipeline look like?
- Husky pre-commit hooks run lint and typecheck, and GitHub Actions then runs matrix tests across Node 18, 20 and 22, a Trivy security scan and a Claude code review in parallel. After merge, Vercel deploys. CI takes about 8 minutes (tests, scan and review) and the Vercel deploy about 3.
- How do I add vulnerability scanning to GitHub Actions?
- Add a Trivy workflow that scans on push, pull request and a weekly schedule, with severity set to CRITICAL,HIGH. Upload the SARIF results to the GitHub Security tab so vulnerabilities show up as code scanning alerts.
- How much does this CI/CD setup cost?
- About $25-30 a month. GitHub Actions is $0 within 2,000 free minutes, Vercel Pro is $20 a month, and the rest is the domain, email and optional monitoring.
- Does the Preact swap work with the Next.js App Router?
- No. The Preact alias only works with the Pages Router and breaks React Server Components, Suspense and the App Router, so skip it on App Router projects.
Related posts
- My Hermes backup said DONE, but a tar exclude dropped every database
My agent backup script printed DONE and uploaded 346 MB. The first restore showed the databases were never in the archive. One tar exclude did it.
- How I track my money with Hermes: the flow, not the numbers
Bank SMS and email alerts flow through one parser, a dedupe hash and a Google Sheet. A morning cron job drafts the summary. Only the flow, no figures.
- Replacing OpenLens: why I kept K9s, Headlamp, and Kubenav
OpenLens is no longer maintained. I tested 13 Kubernetes dashboards and kept three: K9s, Headlamp, and Kubenav.